Where Is Our Data, Really?
"Cyber, But Make It Make Sense" - a Campaign by Cloud Native
The Curious Case of the Data That Went Missing
Nothing was stolen. Nobody hacked the server. So why is your business data turning up in places nobody remembers sending it?
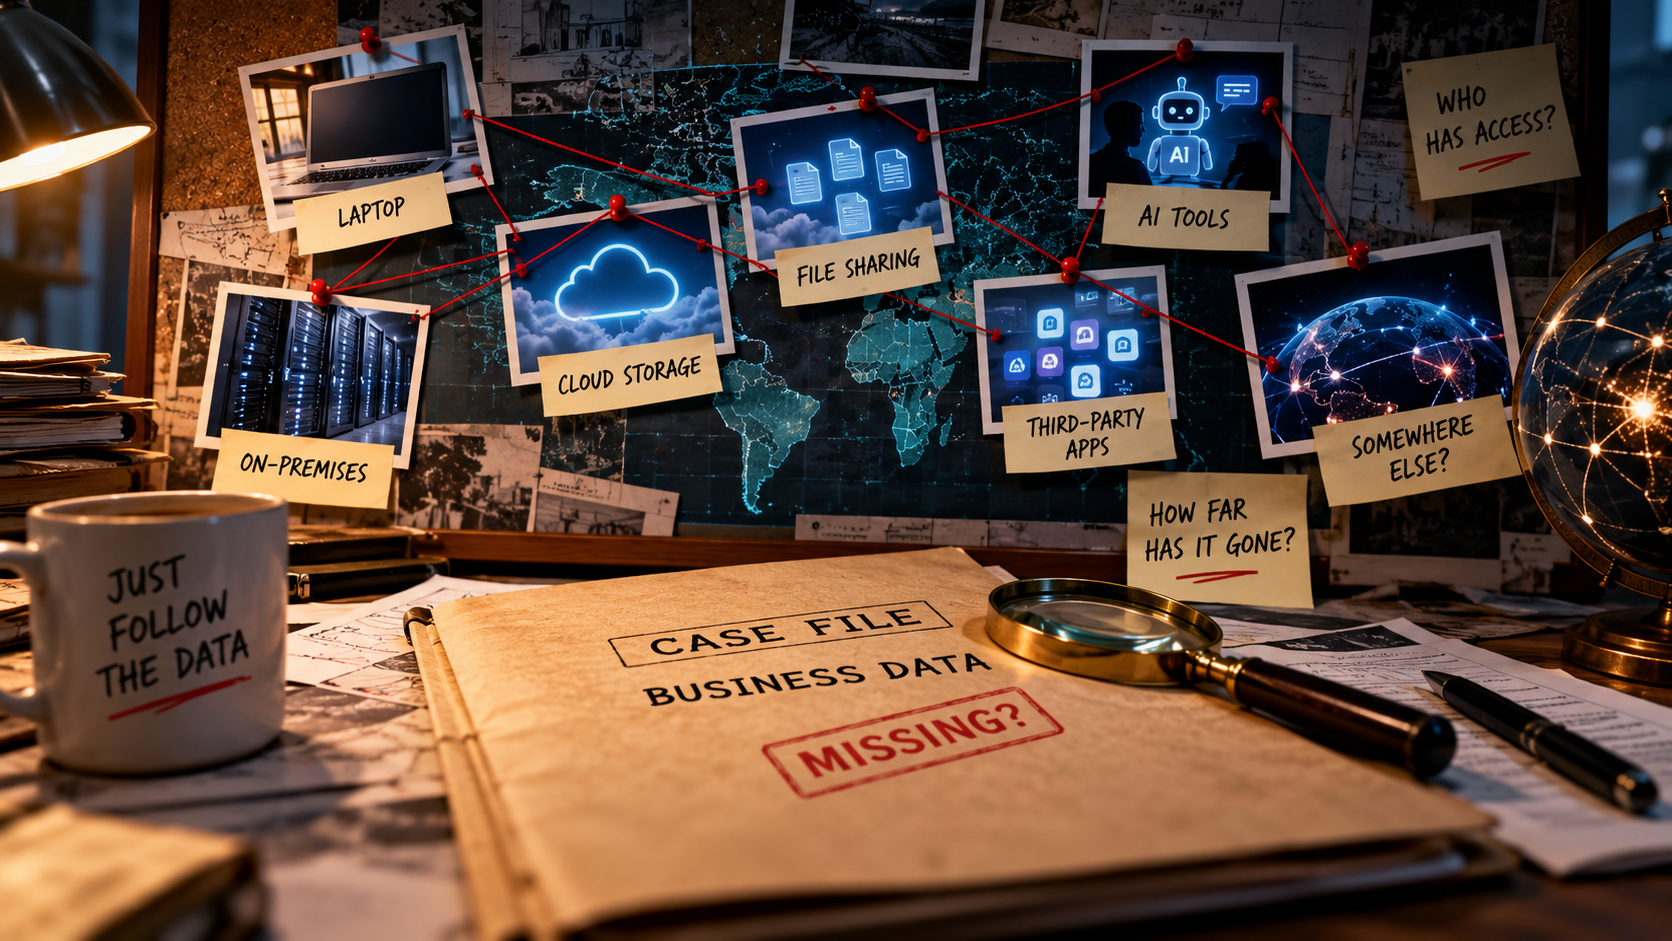
CASE FILE #001
Subject: Business data
Last known location: The company cloud
Current location: Unknown
Persons of interest: Employees, applications, integrations and that AI tool someone started using last Tuesday
Status: Still at large.
Monday morning. You open your laptop, grab a coffee and settle in for a perfectly ordinary day.
Then someone asks a seemingly innocent question:
“Hey, where does all our company data actually live?”
Easy, right? There's the shared drive. The customer database. The business applications. A few cloud platforms.
Case closed.
Except… not quite.
Because somewhere between the shared drive, the spreadsheet someone downloaded, the file someone uploaded to summarise it, and the application connected to another application, your data has been on quite the adventure.
And nobody's keeping a travel diary.
Welcome to the curious case of the data that went missing.
Exhibit A: The file that went on holiday
Let's reconstruct the scene.
At 9:03 am, an employee downloads a customer report from an approved business system.
At 9:07 am, they upload it to an online tool to make the information easier to understand.
At 9:12 am, they copy the results into a presentation.
At 9:20 am, the presentation is shared with a colleague.
By lunchtime, information from one original report may exist across several services and files.
Nothing about this workflow necessarily looks suspicious. The employee is trying to get their work done. The tools might be legitimate, useful and perfectly appropriate for their intended purpose.
But here's the mystery: who knows where all those copies ended up?
The original file may still be exactly where it belongs. Yet the business now has more locations, services and access permissions to consider.
Depending on the tools involved, information might be retained in uploaded files, activity logs, backups or other service records. Deleting the original doesn't automatically delete every copy created elsewhere.
The problem isn't that data moves. Modern businesses need information to move.
The problem is when the business loses sight of the journey.
Exhibit B: The AI assistant with a very good memory
Now, let's introduce our newest person of interest: AI.
Imagine an employee who needs to summarise a lengthy internal report before a meeting. Rather than spending an hour doing it manually, they turn to an AI tool.
They paste in the report. A few seconds later, they have a beautifully organised summary.
Everyone wins.
Well, almost everyone.
Did the report contain customer information? Confidential plans? Financial figures that aren't meant to leave the organisation?
What does the service do with submitted information? How long might it retain it? Who can access it? Are there settings or contractual terms governing whether the information can be used to improve the service?
These questions matter because AI services don't all handle data in the same way. Their practices can vary according to the service, account type, configuration and applicable terms.
Some services offer enterprise controls that differ from their consumer offerings. Some may retain information for particular purposes, even when it isn't used to train a model. Others may have specific deletion, logging or data-location arrangements.
The point is not to assume the worst about AI.
It's to stop assuming anything at all until you've checked.
An employee can have good intentions and still create a data exposure the business hasn't assessed.
And AI isn't the only suspect. Ordinary file-sharing tools, browser extensions, third-party applications and integrations can create similar blind spots.
Convenience isn't the crime. Unexamined data handling is the clue.
Exhibit C: The suspects nobody thought to interview
When businesses investigate where their data lives, they often start with the obvious locations: servers, databases and approved cloud storage.
That's a good start. It just isn't the whole case.
Meet the supporting cast.
The unofficial app. Someone signs up for a free tool because it solves a problem faster than the approved process. The team loves it. IT doesn't know it exists.
The forgotten integration. An application was connected to another service months ago. Nobody remembers what permissions it was granted or whether the connection is still necessary.
The duplicate file. A report has been downloaded, emailed, exported and saved in several folders. Which version is current? Which copies contain sensitive information? Who can still access them?
The departed employee. An employee leaves, but an account, shared folder or third-party connection remains active longer than it should.
The external collaborator. A document is shared with someone outside the organisation. The project ends, but the access remains.
None of these situations automatically means a breach has occurred. But each one raises questions worth investigating.
Who owns this data? Who can access it? Is it still needed here? Are the right protections in place?
If nobody can answer those questions, you've found a visibility gap.
The plot twist: your data isn't actually missing
Here's where our investigation takes an unexpected turn.
In many cases, the data hasn't disappeared at all.
It's sitting exactly where someone put it. The issue is that the business doesn't have a complete picture of where it has travelled, what copies exist or which services have access to it.
This is the difference between data storage and data visibility.
Storage tells you where information is kept.
Visibility helps you understand where information is created, how it moves between systems, who can access it, what happens to it along the way and when it should be removed.
You can have secure storage and still have poor visibility.
You can have excellent security tools and still miss an application nobody knows is being used.
And you can have a perfectly sensible AI policy that doesn't help much if employees don't know it exists — or don't know which tools it applies to.
The goal isn't to eliminate every copy of every file or prevent employees from using useful technology.
It's to make sure the organisation understands and controls the movement of its information.
Case-solving 101: Five questions to follow the data trail
You don't need a room full of investigators and a wall covered in red string. Start with five questions.
1. Where does our important data begin and end up?
Identify the systems that hold your most important information, including customer records, employee information, financial data and commercially sensitive documents.
Then follow the workflows. Where is information exported, uploaded, shared, copied or processed by another service?
Start with the data that would cause the most harm if exposed or mishandled.
2. Which tools are our people actually using?
Don't rely exclusively on the official application list.
Ask teams which tools help them write, analyse, share and organise information. Include AI features embedded in existing applications, as well as services employees may have adopted independently.
The objective isn't to catch people out. It's to understand how work really happens.
3. What happens when information enters another service?
For each relevant service, investigate its data practices.
- What information does it receive?
- Where and how is that information processed?
- Is it retained, and for how long?
- Can it be accessed by other users or service personnel?
- Is it used for additional purposes, such as service improvement or model training?
- What happens when the information or account is deleted?
Check the actual service documentation, account settings and contractual terms. Don't assume that every service has the same answers.
4. Who has the keys?
Review access permissions across the systems involved.
Check user accounts, external sharing, application permissions and integrations. Remove access that is no longer required and apply the principle of least privilege: give people and applications only the access they need.
Where appropriate, use multi-factor authentication and monitor relevant activity.
5. Who is responsible for keeping the map up to date?
Assign ownership for approving tools, reviewing data flows and checking that controls remain appropriate.
When a new application or AI capability is introduced, assess how it handles information before sensitive data starts flowing through it.
Repeat the review when systems change, new integrations are added or business requirements evolve.
Visibility isn't a one-time project. It's an ongoing responsibility.
The Australian connection: this isn't just an IT mystery
Data visibility also matters for privacy and governance.
Australian businesses covered by the Privacy Act need to consider their obligations under the Australian Privacy Principles when handling personal information. Depending on the circumstances, that can include how information is collected, used, disclosed, secured and handled by overseas recipients.
Moving personal information into a third-party service doesn't automatically make the arrangement non-compliant. But it doesn't remove the need to understand the arrangement, either.
The Australian Cyber Security Centre also emphasises that cloud security involves responsibilities shared between the service provider and the customer. Using a cloud service doesn't mean every security decision has been made on your behalf.
Useful starting points:
- Australian Cyber Security Centre — cloud security guidance
- Office of the Australian Information Commissioner — privacy guidance
- Australian Government National AI Centre
These resources can help your organisation assess the relevant security and privacy considerations for its own circumstances.
The final report
After interviewing the suspects, examining the evidence and following the data trail, here's what we've learned.
Your business data doesn't necessarily stay in one place. It moves through people, applications, integrations and services. AI tools add another set of questions to an already complex picture.
That doesn't mean every new tool is dangerous. It means every tool that handles business information deserves the right level of scrutiny.
You don't need to know the location of every file at every second. You do need a reliable understanding of your important data, the systems that process it, the people and services that can access it, and the controls that protect it.
Because the real mystery isn't where your data is stored.
It's whether you know enough about its journey to protect it.
CASE STATUS: Visibility required.
One question for your next team meeting
Ask everyone:
“What's one tool you use to handle work information that our IT or security team might not know about?”
The answer might be completely harmless. It might also reveal your next opportunity to improve visibility.
Either way, it's a much better place to start than waiting for a mystery to become an incident.
Cloud Native — helping make complex technology easier to understand, manage and protect.